
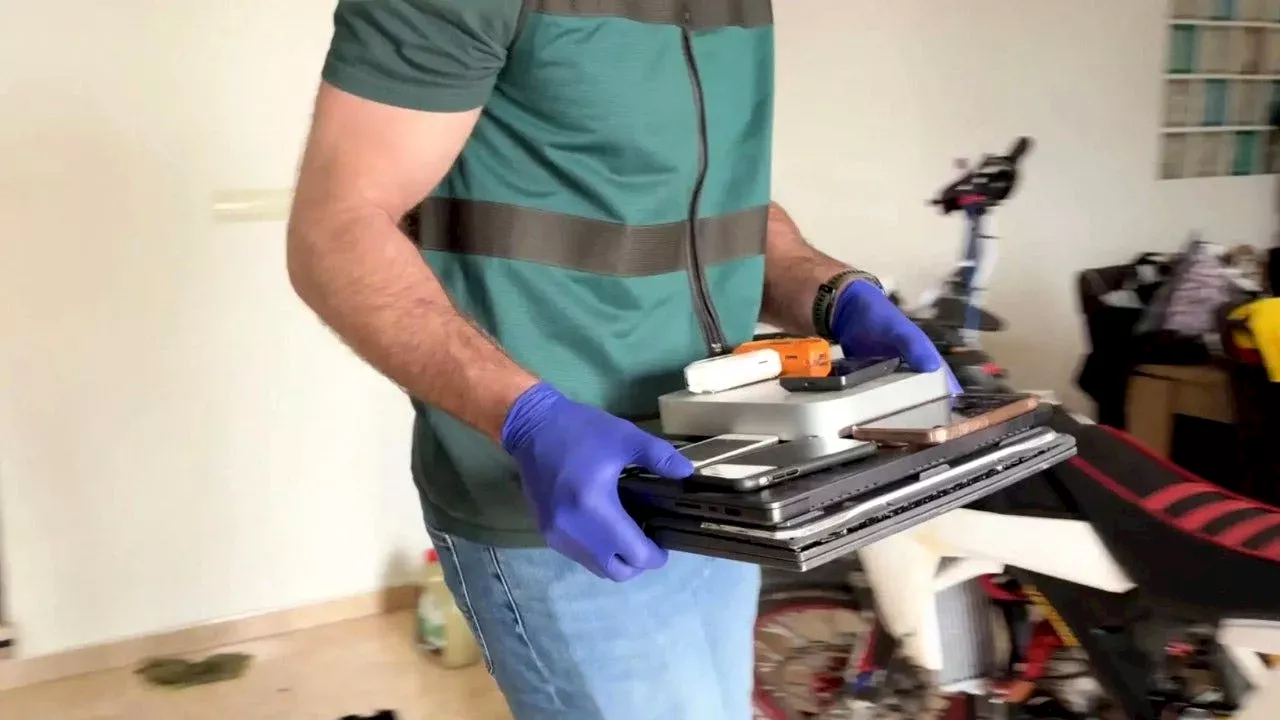
International authorities dismantled the KillSec ransomware operation on September 30, seizing 110 terabytes of stolen data. The crackdown, dubbed Operation KillSwitch, resulted in three arrests and the discovery that a 16-year-old allegedly ran the group.
A 16-year-old administrator at the helm of KillSec
The most jarring revelation from Operation KillSwitch is the age of the suspected leader. According to the report, investigators identified a 16-year-old as the primary operator and administrator of KillSec, a group linked to approximately 1,000 suspected attacks worldwide. This suggests a significant shift in the profile of cybercrime leadership, moving away from seasoned professionals toward tech-native minors.
The operation was not a solo effort, as authorities also identified a developer who turned 18 in August but was a minor during several of the alleged crimes. The group's structure included specialized roles, with investigators identifying individuals suspected of acting as an affiliate and a negotiator to handle ransom demands. These arrests took place across four countries: Greece, Romania, Spain, and the United Kingdom.
110 terabytes of data and 5 central servers seized
Law enforcement agencies, including Europol and Eurojust, successfully neutralized KillSec's core infrastructure by taking control of five central servers. A critical part of this seizure was the group's dark web leak site, which KillSec used to publicly shame victims and threaten the release of sensitive files. By seizing this site, authorities prevented further exposure of stolen information.
The scale of the theft is immense, with at least 110 terabytes of stolen data recovered during the raids. As reported, while KillSec is linked to 1,000 suspected attacks, about 500 of those have been confirmed as successful. This volume of data highlights the group's ability to penetrate diverse organizational networks and extract massive amounts of internal documentation.
How AI tools lowered the barrier for Operation KillSwitch targets
KillSec reportedly utilized artificial intelligence to support its attacks, marking a trend where AI is used to accelerate the reconnaissance and execution phases of cybercrime. This integration of AI means that a teenage operator no longer needs to write every line of malicious code from scratch. Instead,they can leverage AI-assisted tools and stolen credentials to bypass security, effectively lowering the technical barrier to entry for high-impact crime.
This case also illustrates a tactical evolution in ransomware: the shift from simple encryption to data exfiltration. KillSec did not always need to lock a victim's files to create leverage; instead, they stole employee records and confidential business documents. This "double extortion" method ensures that even organizations with perfect backups remain vulnerable to the threat of public data leaks.
Which remaining KillSec affiliates are still at large?
Despite the success of Operation KillSwitch,several critical questions remain. the report notes that the investigation is ongoing, particularly regarding the tracking of cryptocurrency and other criminal proceeds. It remains unclear how many other affiliates were involved in the KillSec ecosystem or if other operators are currently attempting to migrate the stolen data to new servers.
Furthermore, the source does not name the specific organizations targeted in the 500 successful attacks, leaving many potential victims unaware that their data was held by a teenager. because ransomware groups frequently reorganize and resurface under new aliases, the total number of successful attacks may fluctuate as Europol continues to analyze the seized evidence.
Comments 0