
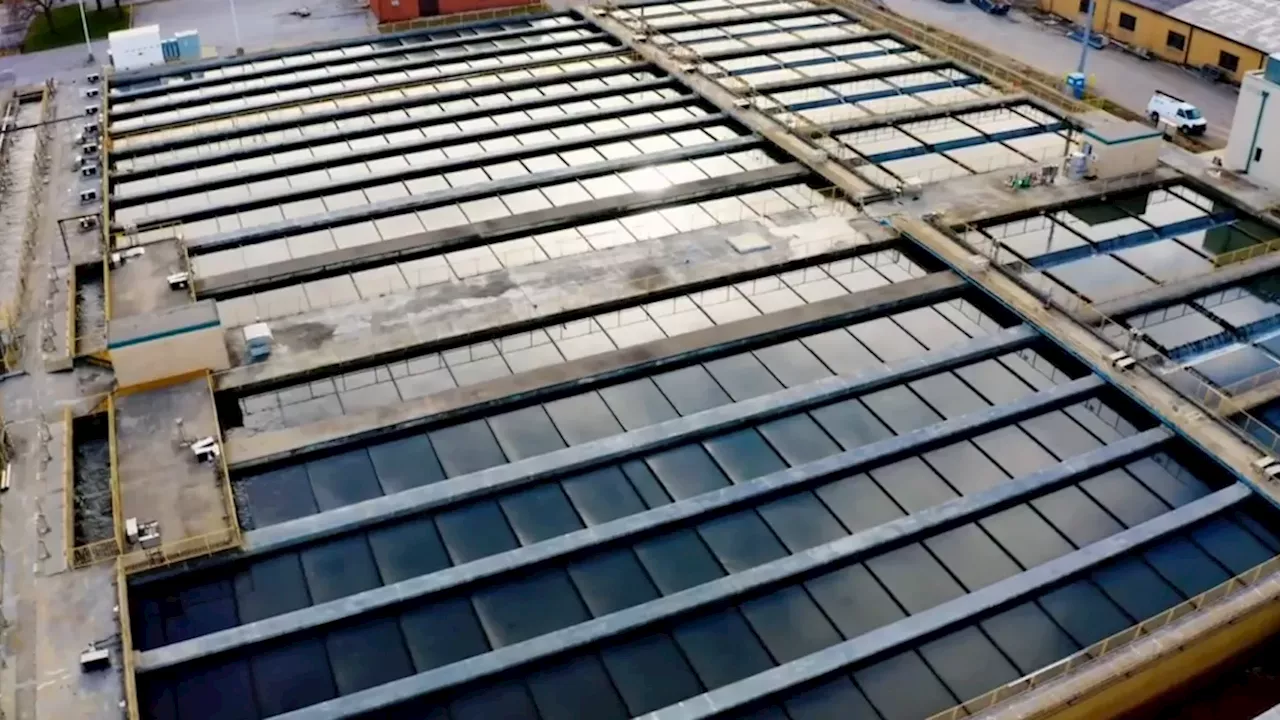
The FBI has issued a federal alert warning that cybercriminals are actively targeting water utilities across the United States. At least 12 states have already reported cyberattacks aimed at disrupting critical drinking water and wastewater infrastructure.
The 12-State Breach and the Threat to Wastewater
According to the report, the FBI has identified a pattern of attacks targeting the controllers that utilize sensors to operate pumps, motors, and valves. These components are the mechanical heart of water distribution; when they are compromised, the physical results are immediate and dangerous. The FBI warns that these intrusions can lead to catastrophic failures, including localized flooding and a significant loss of water pressure.
Beyond simple service outages, the federal government is concerned about the biological safety of the water supply. The FBI has flagged a specific risk where the failure of these systems could allow untreated groundwater to seep into the pipes, potentially contaminating the drinking water available to the public. This shift from data theft to the manipulation of physical hardware marks a dangerous escalation in the nature of infrastructure threats.
Citizens Energy Group's Shield for 900,000 Customers
In Indiana, one of the state's largest utilities, Citizens Energy Group, is moving to harden its defenses to protect its 900,000 customers. As reported by the source, Citizens Energy Group has already implemented the security measures recommended by the FBI, which are considered industry best practices.. The utility is currently coordinating its defense strategy with both the FBI and Indiana's newly established Office of Cybersecurity.
The proactive stance of Citizens Energy Group reflects a broader trend among Indiana utilities to treat cybersecurity as a core operational requirement rather than an IT afterthought.. Other entities, such as Indiana American Water, are reportedly taking continuous steps to strengthen their systems, while the City of Carmel is collaborating with the federal government to conduct a comprehensive utilities assessment.
The Geopolitical Shift Toward Targeting US Water Infrastructure
Cyber experts suggest that these attacks on water utilities are not isolated criminal acts but are increasingly becoming part of broader geopolitical cyber conflicts.. By tarrgeting the basic necessities of life—water and sanitation—adversaries can create widespread panic and instability without firing a single shot. this trend mirrors previous attacks on energy grids and pipelines, suggesting that water is the next frontier in hybrid warfare.
The vulnerability of these systems often stems from the integration of legacy industrial equipment with modern networking. As utilities attempt to modernize their monitoring capabilities, they often inadvertently expose critical controls to the public internet, creating an entry point for state-sponsored actors or sophisticated criminal syndicates.
The Gap Between Internet-Facing Devices and Critical Controls
To mitigate these risks,the FBI has provided a specific set of recommendations for utilities, most notably the requirement to separate critical utility controls from internet-facing devices. this "air-gapping" or segmentation prevents a hacker who gains access to a corporate email or a billing system from jumping over to the pumps and valves that control the water flow. The FBI also emphasized the necessity of regularly updating security software to patch known vulnerabilities.
Despite the urgency of the alert, several critical details remain missing from the public record. the FBI has not specified which 12 states were targeted, nor has it named the specific "bad actors" or nation-states responsible for the incursions. Furthermore, it remains unclear whether any of the reported attacks in those 12 states actually resulted in the seepage of untreated groundwater, or if that remains a theoretical risk that the FBI is attempting to preempt.
Comments 0