
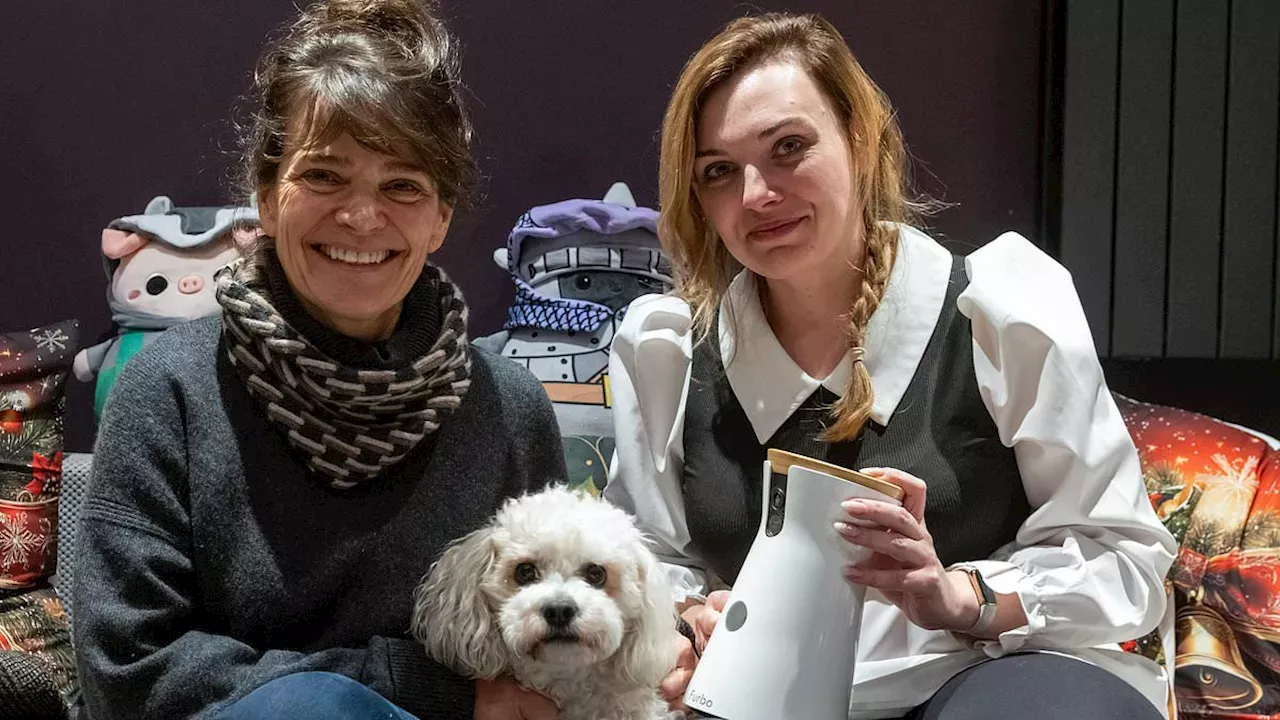
In the West London suburb of Harefield, 36-year-old Julia Starzyk has spent eight years building a highly automated living environment. while her home offers extreme convenience, a recent report highlights how these connected devices create significant privacy risks by transmitting personal data to third parties and overseas servers in China.
The Eight-Year Evolution of a Harefield Smart Home
The Starzyk residence is a showcase of modern automation, where nearly every convenience is linked to the internet. As the report describes, the home is a place of meticulous order, where even the windows and toilet paper are kept in pristine condition. This obsession with neatness is supported by an array of integrated systems, including:
- Smart central heating and underfloor heating
- Security cameras and garden watering systems
- Robot dogs that dispense treats to her dog, Susan
- Air-freshening bulbs and smart appliances
For Starzyk, these gadgets provide a sense of safety and meticulous control over her environment, allowing her to manage almost every system directly from her smartphone .
Data Flows to Third Parties and Chinese Servers
The high level of connectivity in the Harefield home comes with a significant digital cost. The report notes that the sensors, microphones, and cameras installed throughout the house do more than just provide convenience; they constantly harvest data on Starzyk's daily routines. This information—which includes movement logs, audio recordings, and video footage—is not merely stored on local devices.
Instead, this data is transmitted to various third-party companies and, most notably, to overseas servers located in China. This data harvesting can turn innocuous habits, such as when Starzyk eats or the exact timing of her sleep schedule, into valuable commodities for targeted advertising and other commercial purposes.
The Samsung TV and the @log4j Surveillance Discovery
Specific vulnerabilities in consumer electronics have already been demonstrated by independent researchers. According to the report, a researcher known as @log4j recently exposed how a Samsung television was utilizing automatic content recognition technology to secretly listen to background noises. This data was then relayed to marketers, illustrating how a central household device can act as a listening post.
This same risk applies to the dozens of other connected appliances, from air fryers to coffee makers, that populate Starzyk's home. Each device represents a potential point of data leakage that the user may not fully perceive.
Andrew Laughlin’s Warning and the Question of User Consent
Security experts are increasingly concerned about the "back-doors" created by the proliferation of smart gadgets.. Andrew Laughlin of Which? has warned that each connected application provides a potential entry point for cyber-attacks, as the high value of personal information attracts opportunistic breaches. Laughlin suggests that as the number of devices grows, the complexity of securing a home increases exponentially.
This leads to several critical, unanswered questions regarding the current state of smart home security. It remains unclear how much actual oversight these third-party companies provide once data is transmitted, and whether consumers like Starzyk can truly provide informed consent when the full extent of data relaying is so opaque. Furthermore, the report leaves it unverified whether the specific data harvested from Starzyk's home has already been compromised by malicious actors.
Comments 0