
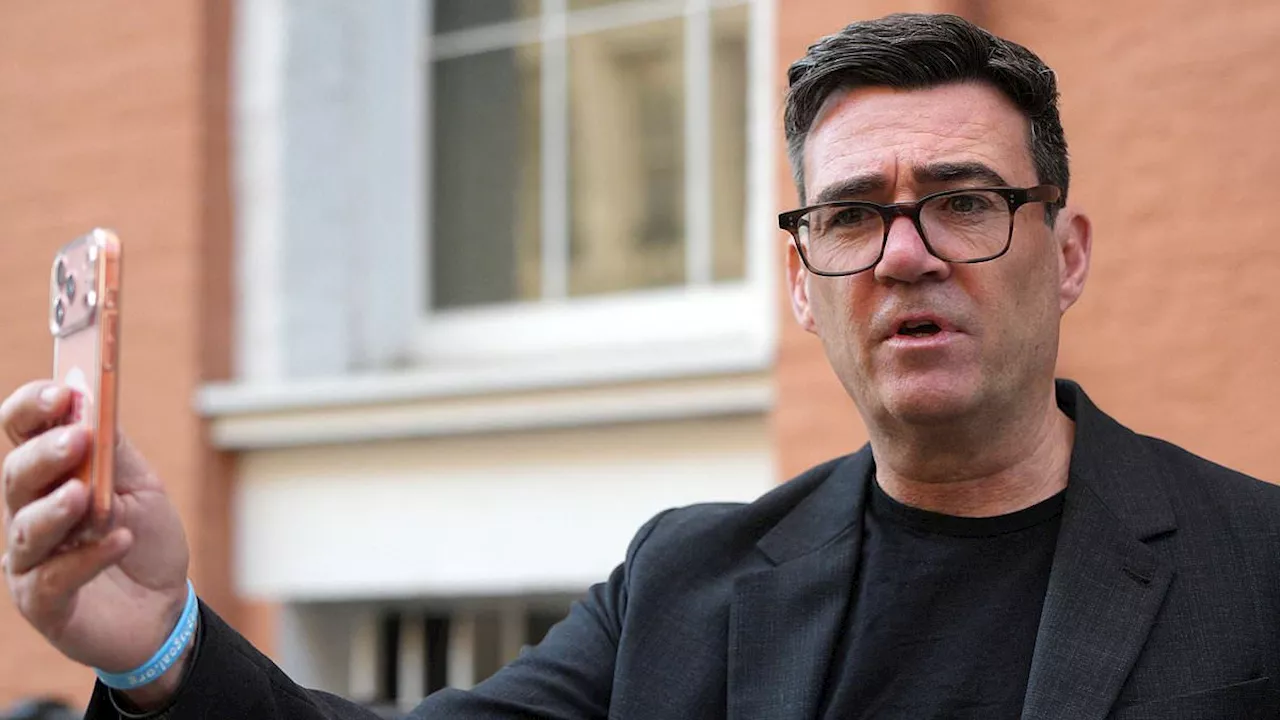
British Prime Minister Andy Burnham was recently tricked by an imposter pretending to be Susie Wiles, the chief of staff for Donald Trump. the incident, which involved several days of text messaging, has triggered an international investigation into the identity of the hoaxer.
The Susie Wiles text hoax targeting Andy Burnham
The text message exchange occurred over several days, spanning the period just before and after Andy Burnham officially entered Downing Street. As reported by Politico, the Prime Minister believed he was communicating with the high-level Trump aide, but was actually messaging a fraudulent account. While sources close to the situation insist that the messages exchanged were of no political significance, the breach was serious enough that the British embassy in Washington felt compelled to alert the White House.
The incident has raised questions regarding the protocols used by the Prime Minister's office during such a sensitive transition of power. Although no telephone conversations took place, the fact that a sitting Prime Minister was engaged in a multi-day digital dialogue with a fake identity has caused significant concern within the UK government.
From AI voice cloning to leaked Cabinet numbers
Susie Wiles has been a recurring target for sophisticated cyber-attacks, making this latest impersonation particularly alarming. In May, Wiles' phone was reportedly hacked by an individual who utilized AI to replicate her voice during calls with prominent Republican officials. Furthermore, the report notes that a cyber espionage unit linked to Iran's Revolutionary Guards targeted her in 2024.
Security vulnerabilities appear to extend well beyond the Prime Minister's immediate circle. It was recently discovered that the personal mobile numbers for at least three UK Cabinet ministers—including Defence Secretary Wes Streeting, Justice Secretary Alex Norris, and Northern Ireland Secretary Chris Bryant—were available for public viewing online. While these numbers were removed after being flagged, the exposure highlights a persistent weakness in how senior officials protect their digital footprints.
Why Professor Anthony Glees calls the breach a 'bullseye'
Professor Anthony Glees,a seucrity and intelligence expert from the University of Buckingham, has characterized the incident as a major security failure. Glees argued that the hoax represents a "bullseye" in terms of successful targeting, noting that it is a poor start for Burnham's efforts to establish himself on the global stage. He specifically questioned why agencies such as GCHQ and the FBI did not prevent the Prime Minister from being compromisd.
The critique from Glees emphasizes that this was not merely a conversation between two low-level civil servants, but a dialogue occurring as a world leader took the reins of power. According to the report, the inability to verify the identity of a key US official during such a critical window suggests a breakdown in the expected chain of secure communications.
The debate between a US-based hoaxer and Tehran's playbook
The origin of the hoax remains a central unanswered question for investigators. Security experts have suggested that the tactics used by the imposter could be modeled after methods frequently employed by Tehran. However, Whitehall sources have offered a different perspectiive, suggesting the orchestration may have originated within the United States rather than abroad.
Several critical details remain unverified, including the true identity of the perpetrator and whether the imposter gained access to any sensitive information through the text thread. additionally, while the White House has been notified, it remains unclear if the US government will launch a joint investigation with British intelligence to determine if this was a state-sponsored operation or a localized criminal act.
Comments 0