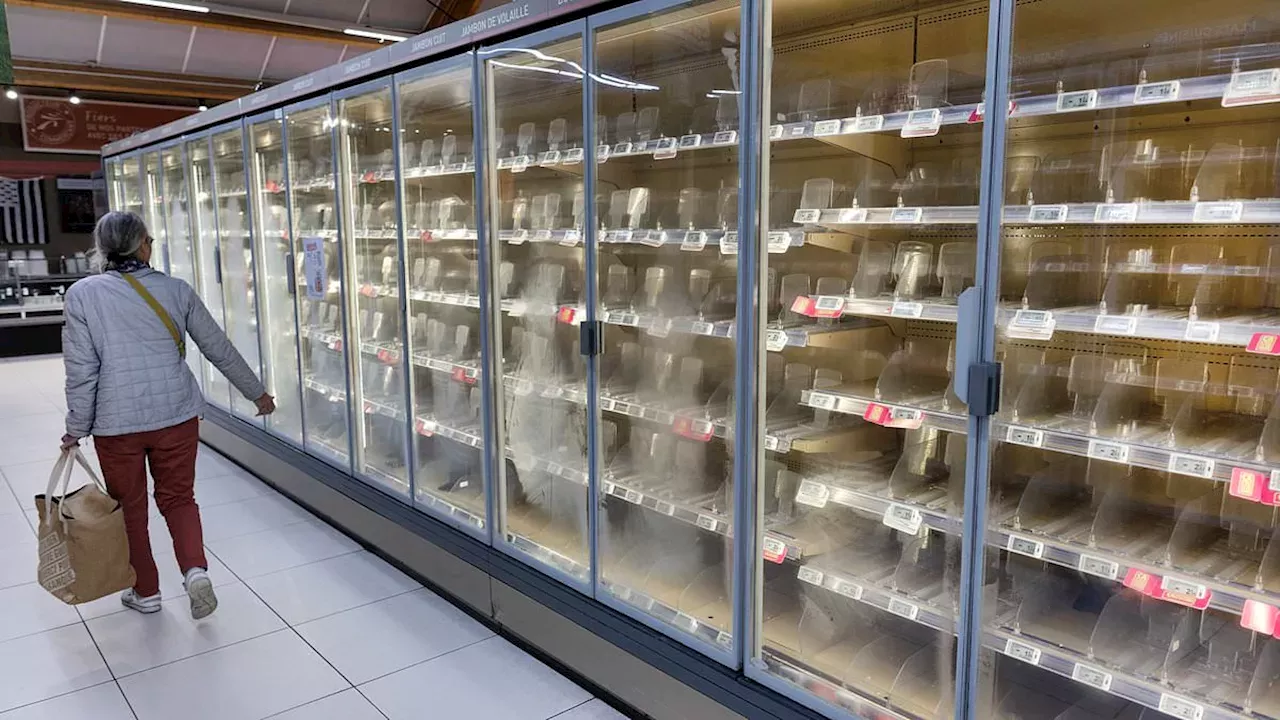
EU cybersecurity chief Juhan Lepassaar has cautioned that home devices could be targeted after hackers disabled commercial refrigerators across Europe. These attacks, which hit hundreds of stores in October,caused massive food spoilage and have been linked by French officials to Iran.
The 50C Heatwave that Cost French Retailers Millions
On October 11, hackers executed a coordinated strike against commercial refrigeration units across more than 700 retailers in France. according to the report, the attackers manually overrode temperature controls, programming systems to blast hot air at 50C, which drove internal fridge temperatures up to 36C. This caused a catastrophic loss of produce, including meat and ice cream, and in some extreme cases, the units caught fire.
The scale of the disruption was widespread, affecting major brands such as Carrefour, Monoprix, Intermarche, and Cooperative U. one French supermarket owner estimated that the financial damage resultting from the perished inventory and equipment failure could reach tens of millions of euros nationwide.
The Shahid Kaveh Group and the Iranian Connection
French authorities have pointed to the Shahid Kaveh Group, an elite cyber unit linked to Iran's Revolutionary Guards,as the orchestrator of the breaches. As the report says,the Paris prosecutor's office identified a methodology characteristic of this group, supported by the discovery of Farsi language in the code and IP addresses tracing back to devices located in Iran.
In response to these findings, French Foreign Minister Jean-Noel Barrot summoned the Iranian ambassador to the Foreign Ministry in Paris. Barrot has threatened further EU sanctions against Iran, asserting that there will be consequences for the state-aligned sabotage.
From US Military Commissaries to European Blood Banks
The sabotage of European food chains is part of a larger pattern of targeting cold-storage infrastructure. the report notes that in August, refrigerators in at least half a dozen US military commissaries malfunctioned in a manner that Pentagon investigators are treating as a suspected cyber attack. The Pentagon currently considers Iran a primary suspect in those August incidents, though the investigation remains ongoing.
The vulnerability extended beyond supermarkets during a second wave of attacks this month, which hit more than 100 establishments across Europe. This wave specifically impacted French blood banks,forcing medical staff to urgently relocate blood supplies to alternative cold storage units to prevent the loss of life-saving resources.
The Silence of Iran's UN Mission and the Pentagon's Pending Proof
Despite the specific accusations from Paris, several critical pieces of information remain unverified. Iran's mission to the United Nations has not responded to requests for comment, and Tehran continues to routinely deny involvement in malicious cyber operations. Furthermore, while the Pentagon has acknowledged the speculation regarding the US commissary hacks, military investigators have declined to provide specific evidence for security reasons.
The Outdated Firmware Vulnerability in Home Routers
Juhan Lepassaar, the executive director of the EU's cybersecurity agency, warned in Brussels that the same vulnerabilities exploited in supermarkets could be used to target home routers and appliances. The firm responsible for many of the breached commercial units admitted that several devices were obsolete or running outdated firmware, making them easy targets for entry.
Lepassaar emphasized that while state-aligned actors from Russia, China, North Korea, and Iran frequently target Europe, these incidents are avoidable through investment. He argued that security cannot be an afterthought for connected devices, though he acknowledged that implementing robust cybersecurity across the continent is an expensive undertaking.
Comments 0