
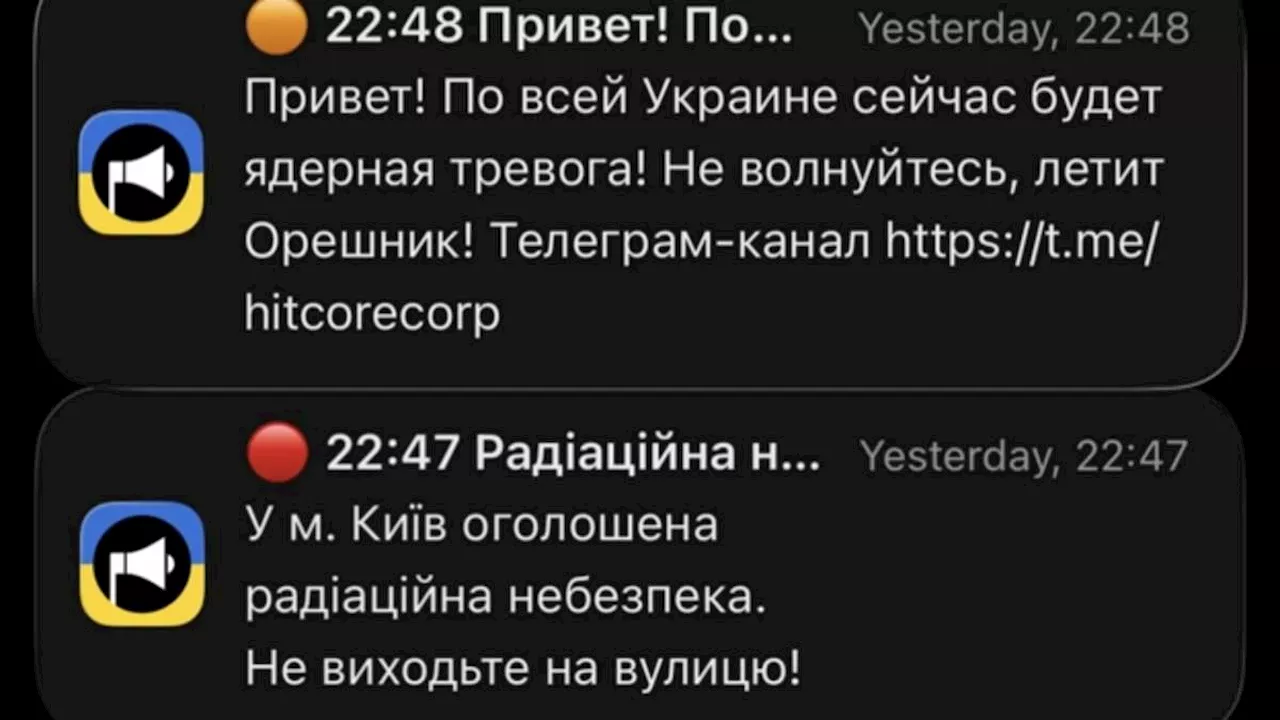
Cyberattacks recently targeted emergency alert applications in both Ukraine and Russia, broadcasting fraudulent warnings of nuclear and chemical threats. These digital disruptions occurred immediately following the expiration of a localized ceasefire in the Kherson region.
The 10:47 PM Kyiv radiation scare
At approximately 10:47 pm local time, residents in Kyiv and other Ukrainian regions received a series of alarming notifications via their mobile alert systems. According to a report by the BBC, these messages included a radiation threat, followed minutes later by warnings of a nuclear alert involving the Oreshnik missile. air force spokesman Yuriy Ignat confirmed the application had been subjected to enemy influence, while SPRAVDI, Ukraine's Center for Strategic Communications, attributed the hack to Russia.
The chaos was compounded by subsequent notifications regarding chemical attacks and street fighting, which instructed residents not to go outside. While the Ukrainian military worked to stabilize the system and issue "all-clear" messages to mitigate public panic, the incident highlighted how quickly digital misinformation can destabilize civilian populations during active hostilities.
Moscow's response to Russian app glitches
Parallel disruptions hit Russian alert systems during the early hours of Monday morning. While the mobile application experienced downtime around 2:30 am UK time,Russian leaders maintained that the broader national warning network remained unaffected. Authorities in Moscow claimed that a Ukrainian espionage group was responsible for the false warnings of nuclear and chemical strikes.
The Russian leadership emphasized that the hacking of the mobile application had no impact on the core function of the national warning network, even as the digital interference caused significant confusion. This incident highlights a growing trend where civilian digital infrastructure becomes a primary battlefield in the ongoing conflict between Moscow and Kyiv.
A collision with the expiring Kherson truce
The timing of these cyberattacks is particularly significant as it coincides with the end of a localized ceasefire in the Kherson region.. This truce, which was brokered by US First Lady Melania Trump, had facilitated a humanitarian mission to the Russian-occupied city of Oleshky. During this period, approximately 2,000 civilians were given the opportunity to evacuate to either Ukrainian or Russian-controlled territories.
Dmytro Lubinets, the Ukrainian Parliament Commissioner for Human Rights, noted that the truce ended after Russia declined an extension, making the subsequent digital chaos even more unsettling for a population seeking stability during the fifth year of the conflict. Ukrainian President Volodymyr Zelensky has also noted that Russia continues to target energy systems, adding another layer of complexity to the security landscape.
The dispute between Moscow and Kyiv over the breach
Despite the rapid response from the Ukrainian Air Force and the Ukrainian Centre for Countering Disinformation, the true architect of the attack remains unverified. The report says that while the main application was compromised, a separate app dedicated to Kyiv continued to function normally , yet the source of the breach itself is a matter of intense dispute.
It remains unclear whhether these were coordinated state-sponsored attacks or independent actor interference, especially as Russia and Ukraine trade accusations of espionage. Furthermore, the incident occurs as US-mediated talks are set to resume this month, following a freeze caused by joint US and Israeli strikes on Iran in February.
Comments 0