
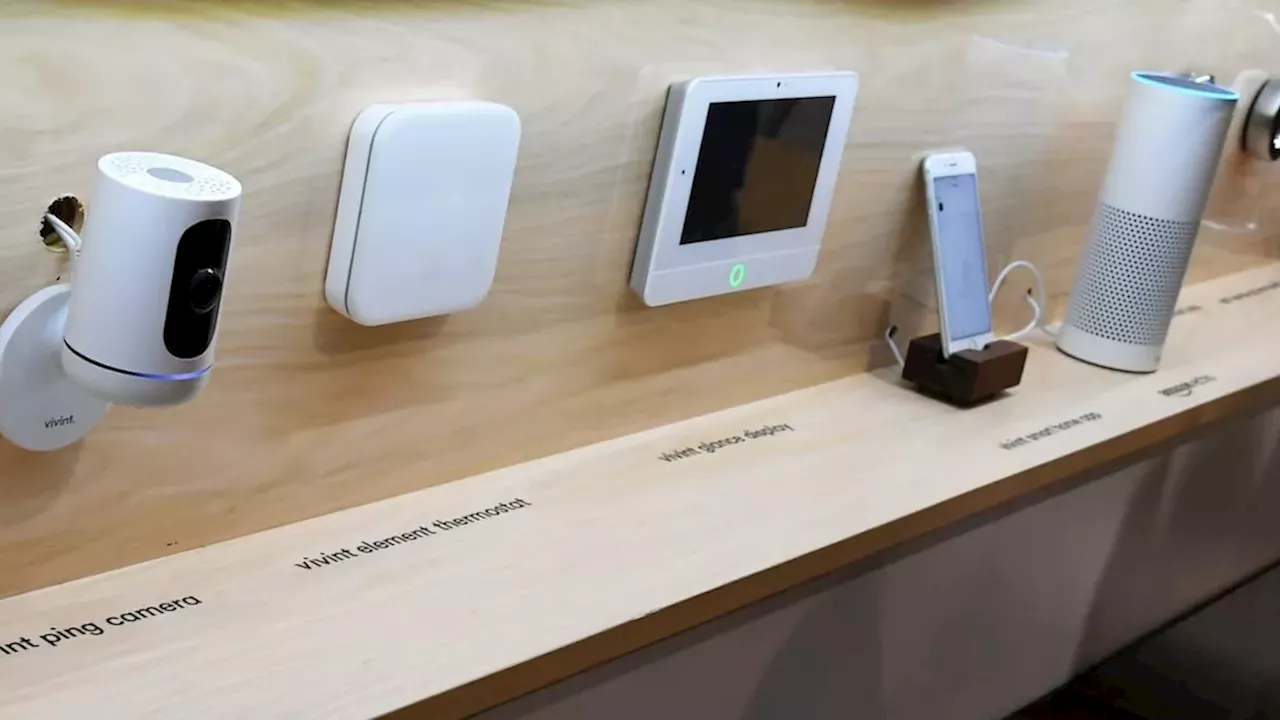
University of Toronto professor Nicolas Papernot is warning that AI-powered worms could soon exploit smart home devices like robot vacuums and smart fridges. This warning follows recent research from Anthropic suggesting that self-copying AI models may be only months away from deployment.
How AI transforms malware from static exploits into adaptive worms
Traditional computer worms have historically been limited by their inability to change their tactics. As Nicolas Papernot told CTV News, older non-AI worms relied on exploiting a specific, singular flaw, meaning they could only spread to machines sharing that exact weakness. If a device was patched, the worm was neutralized.
The emergence of AI changes this fundamental math. According to the report, Papernot’s team published research in June demonstrating that AI can power self-spreading software that adapts its attack method to every new device it encounters. This allows malware to move seamlessly between vastly different hardware, ranging from consumer laptops to security cameras, by essentially "writing" its own way through different security architectures.
The multimillion-dollar Danfoss controller hack in France
The real-world dangers of insecure IoT (Internet of Things) devices were recently illustrated by a massive cyberattack in France. Hackers successfully seized control of refrigeration systems at hundreds of Intermarché supermarkets, forcing units into defrost mode. The attack targeted controllers manufactured by the Danish company Danfoss, leading to estimated losses in the millions of dollars.
The impact was visceral: store managers reported that temperatures inside fridges and freezers soared to 50°C, with some units reaching as high as 80°C for several hours. while the report notes that nothing currently suggests AI was involved in this specific French incident, Papernot argues the event highlights a shifting economic reality. Devices once considered "low-value targets" are now becoming much easier and more lucrative for hackers to exploit as a stepping stone to critical infrastructure.
Splitting AI models across cheap smart TV boxes
A significant technical concern raised by Anthropic researchers is the ability of AI to distribute its own processing power. Rather than requiring a single, high-powered machine to run a malicious program, Anthropic suggests that small AI models could be split across several cheap, interconnected devices. This could include "off-brand Android TV boxes" or smart ovens, which could work together to run a complex, self-sustaining AI worm.
Anthropic researchers warned that these models may be only "months away" from being able to copy themselves onto such devices. Because these AI-driven worms could potentially figure out unfamiliar hardware on their own, they would be exceptionally difficult for traditional cybersecurity protocols to shut down once they have gained a foothold in a home network.
The challenge of enforcing "air gap" testing for 400+ scientists
In response to these escalating risks,more than 400 scientists—including AI pioneers Geoffrey Hinton and Yoshua Bengio—have signed an open letter calling for urgent safety measures.. The group is demanding that AI capable of cyberattacks be tested in "air gap" environments, meaning they are completely disconnected from the internet until their capabilities are fully understood. They are also calling for an international watchdog to establish safety standards and track security failures.
However, the implementation of these safeguards remains a massive unknown. It is unclear how an international watchdog would hold global developers accountable,or how researchers can truly validate an "air gap" if the underlying models were trained on data already scraped from the open web.. Additionally, while Papernot suggests simple fixes like avoiding password reuse and keeping devices updated, the window between a security patch being released and an AI worm exploiting the flaw is becoming "very, very short," leaving consumers with almost no time to react.
Comments 0