
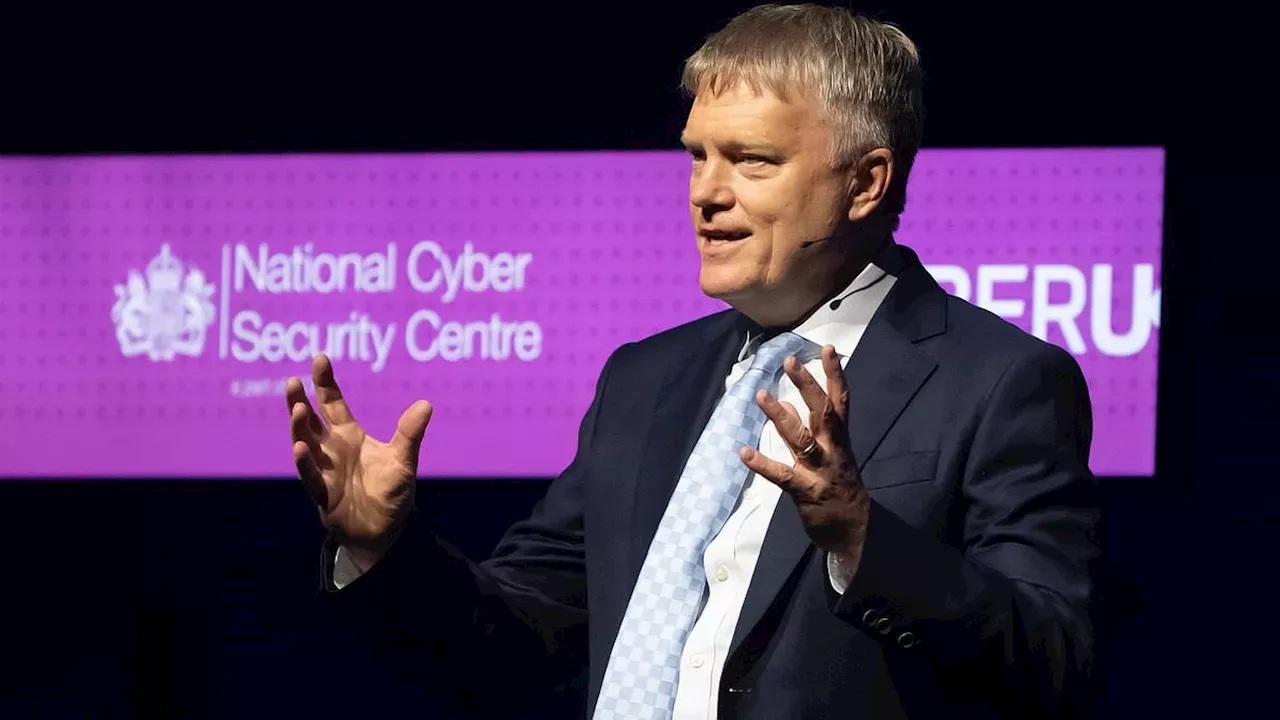
Richard Horne, head of the UK's National Cyber Security Centre (NCSC), has warned that hostile state actors will likely use artificial intelligence to target critical infrastructure by 2028. the alert highlights a looming threat to essential services, including energy supplies, defense, and transport networks.
The 2028 Deadline for Russia and China's AI Offensive
The National Cyber Security Centre predicts that by 2028, nation-states such as Russia and China will routinely integrate artificial intelligence into their cyber warfare toolkits to achieve geopolitical goals. According to the NCSC, these actors are not necessarily inventing entirely new forms of attack, but are instead using AI to execute known tactics—such as ransomware—with a speed and scale that was previously impossible for human operators.
This shift represents a fundamental change in the threat landscape. By lowering the cost and technical barriers to entry, AI allows state-sponsored hackers to probe thousands of systems simultaneously , identifying the path of least resistance in seconds. The NCSC suggests that the window for the United Kingdom to harden its defenses is closing rapidly as these capabilities mature.
Unpatched Software and Weak Passwords as AI Force Multipliers
A primary concern cited in the NCSC's State of the Cyber Nation report is that the UK's current resilience is insufficient because of "preventable weaknesses." The report specifically flags the persistence of unpatched software and the use of weak password protection across various organizations as critical vulnerabilities. When combined with AI, these basic security failures become high-speed entry points for malicious actors.
This trend reflects a broader global struggle where the pace of offensive AI development is significantly outstripping the adoption of defensive security hygiene. For many organizations, digital risk is treated as a secondary IT concern rather than a core business risk. The NCSC argues that this negligence provides the raw material that AI-driven attacks need to succeed,turning simple oversight into a national security liability.
From Jaguar Land Rover to Binance: The Cost of Digital Fragility
The warnings from Richard Horne are grounded in recent, tangible failures across the global economy. As reported by the NCSC, the largest recorded hack involving the cryptocurrency firm Binance and disruptions to European refrigeration systems—which threatened food supplies—demonstrate the systemic risk of digital dependency. These incidents prove that cyber attacks have moved beyond data theft and into the realm of physical and economic disruption.
Closer to home, the UK has alerady seen the impact of such breaches; Jaguar Land Rover suffered significant production halts last year following a breach of its computer systems. These examples serve as a blueprint for what a coordinated, AI-enhanced attack on the UK's energy or transport grids could look like, where the goal is not just espionage, but the total cessation of critical services.
Richard Horne's Call for a National Security Pillar
To counter these threats, Richard Horne is urging organizational leaders to stop treating cybersecurity as an afterthought and instead establish it as a fundamental pillar of national strength. The NCSC asserts that the UK is at a strategic crossroads: it must either invest urgently in resilience or accept a future of increasingly frequent and costly systemic failures.
However, several critical details remain unclear in the NCSC's public warnings. While the agency names Russia and China,it has not specified which particular AI models or frameworks are most concerning. Furthermore, the report does not outline a specific funding mechanism or regulatory mandate to force lagging organizations to patch the "preventable weaknesses" mentioned.. It remains to be seen whether the UK government will move from issuing warnings to imposing strict security mandates on the private operators of critical infrastructure.
Comments 0