
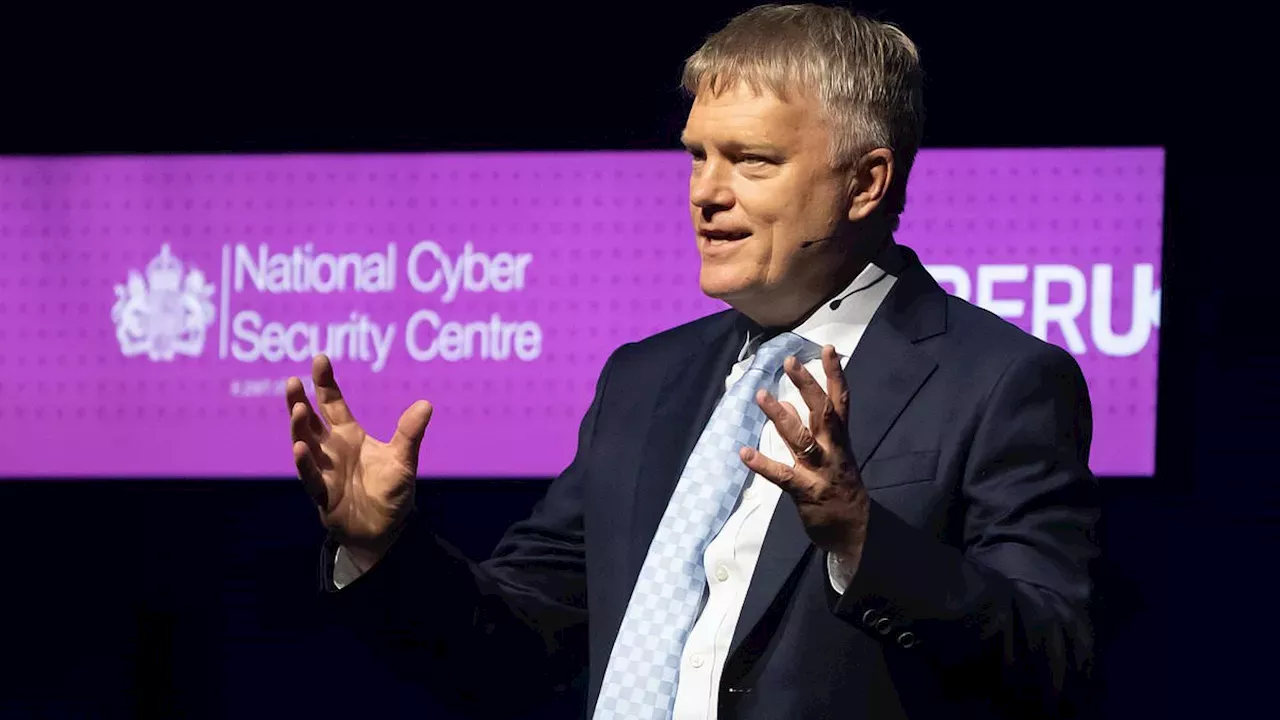
Richard Horne, head of the National Cyber Security Centre, has warned that Russia and China are expected to deploy AI-driven cyberattacks against the UK's critical infrastructure by 2028. The alert emphasizes a critical need for the UK to modernize its defenses to prevent widespread disruption of essential services.
The 2028 Deadline for Russia and China's AI Offensive
The National Cyber Security Centre (NCSC) has established a four-year window before artificial intelligence becomes a routine tool for hostile nation-states. According to the NCSC, it is highly probable that Russia and China will integrate AI into their cyber operations to achieve specific geopolitical goals by 2028. This shift is expected to dramatically increase both the velocity and the scale of attacks targeting the United Kingdom's most sensitive systems.
This timeline suggests that the digital arms race has entered a phase where the ability to automate complex intrusions is no longer a theoretical risk but an imminent operational reality.. The NCSC warns that the window to fortify national defenses is closing rapidly as these AI capabilities become more accessible to state-sponsored actors.
Why the 'State of the Cyber Nation' Report Flags a Defensive Lag
A critical imbalance currently exists between the sophistication of global threats and the UK's readiness. The annual State of the Cyber Nation report indicates that the growth of cyber threats has significantly outpaced the nation's defensive evolution. Richard Horne noted that the UK's current level of resilience is not where it needs to be, creating a dangerous gap that adversaries can exploit.
This vulnerability is part of a broader global trend where state-level actors leverage asymmetric advantages to bypass traditional security perimeters. For the UK, this means that while the threats are evolving toward AI-driven autonomy, many domestic organizations are still struggling with legacy systems and outdated security protocols.
How AI-Powered Malware Lowers the Cost of Infrastructure Attacks
Artificial intelligence is fundamentally altering the economics of cyber warfare by making sophisticated attacks faster and cheaper to execute. As the NCSC reported, AI allows adversaries to identify and exploit systemic weaknesses at a scale that was previously impossible for most threat actors.. This capability is expected to manifest in a surge of AI-powered malware and ransomware targeting critical national infrastructure between now and 2028.
By lowering the barrier to entry for complex operations, AI enables hostile actors to conduct mass-scale reconnaissance and precision strikes with minimal manual effort. This technological leap means that vulnerabilities which once required months of human analysis can now be discovered and weaponized in a fraction of the time.
From Jaguar Land Rover to Binance: The Physical Cost of Digital Gaps
The NCSC's warnings are grounded in recent precedents where digital breaches resulted in tangible economic and physical disruption. The report cites the massive cyber attack on the cryptocurrency firm Binance and intrusions into European refrigeration systems that threatened food supplies as evidence of the systemic risk. furthermore, the breach of Jaguar Land Rover's computer systems last year crippled vehicle production, demonstrating how a digital failure can halt industrial output.
These incidents illustrate that the target is rarely just data; the goal is often the disruption of physical processes. Whether it is the automotive supply chain or the food cold-chain, the transition from a software breach to a real-world crisis is now a proven pathway for attackers.
Which 'Basic Security Hygiene' Failures Still Plague the UK?
Despite the looming threat of AI, Richard Horne highlighted that many UK organizations are failing at the most fundamental levels of security.. The NCSC report points to unpatched software and poor password protection as prevalent weaknesses that leave essential services exposed. This suggests that the UK's vulnerability is not just a lack of advanced AI defenses, but a failure to implement basic security hygiene.
However, the report leaves several key questions unanswered. It remains unclear which specific sectors of the critical national infrastructure are the most neglected in terms of patching. Additionally, the NCSC has not specified whether the current lag in resilience is due to a lack of fudning, a shortage of skilled cybersecurity personnel, or a lack of regulatory enforcement across private-sector infrastructure providers.
Comments 0