
On July 30, 2026, a coordinated cyberattack disabled water services for 190,000 people across 37 Minnesota municipalities. The breach targeted operational technology, forcing the state to issue boil water advisories while emergency crews worked to restore pipeline pressure.
The SCADA vulnerability that silenced 37 utilities
The disruption was caused by a sophisticated threat actor who exploited an unpatched vulnerability within a widely used SCADA software platform.. According to the report, this allowed the attacker to penetrate the Programmable Logic Controller (PLC) grids, which are the systems responsible for the real-time flow of water. By sending forged commands, the attacker forced critical pumps to isolate and valves to close.
This technical failure triggered automated safety protocols that immediately cut off water distribution. The Minnesota Public Utility Commission is now responding by mandating the adoption of network segmentation and the deployment of hardened PLC firmware updates to prevent similar command-forgery attacks in the future.
How 190,000 residents and the city of Plymouth lost water
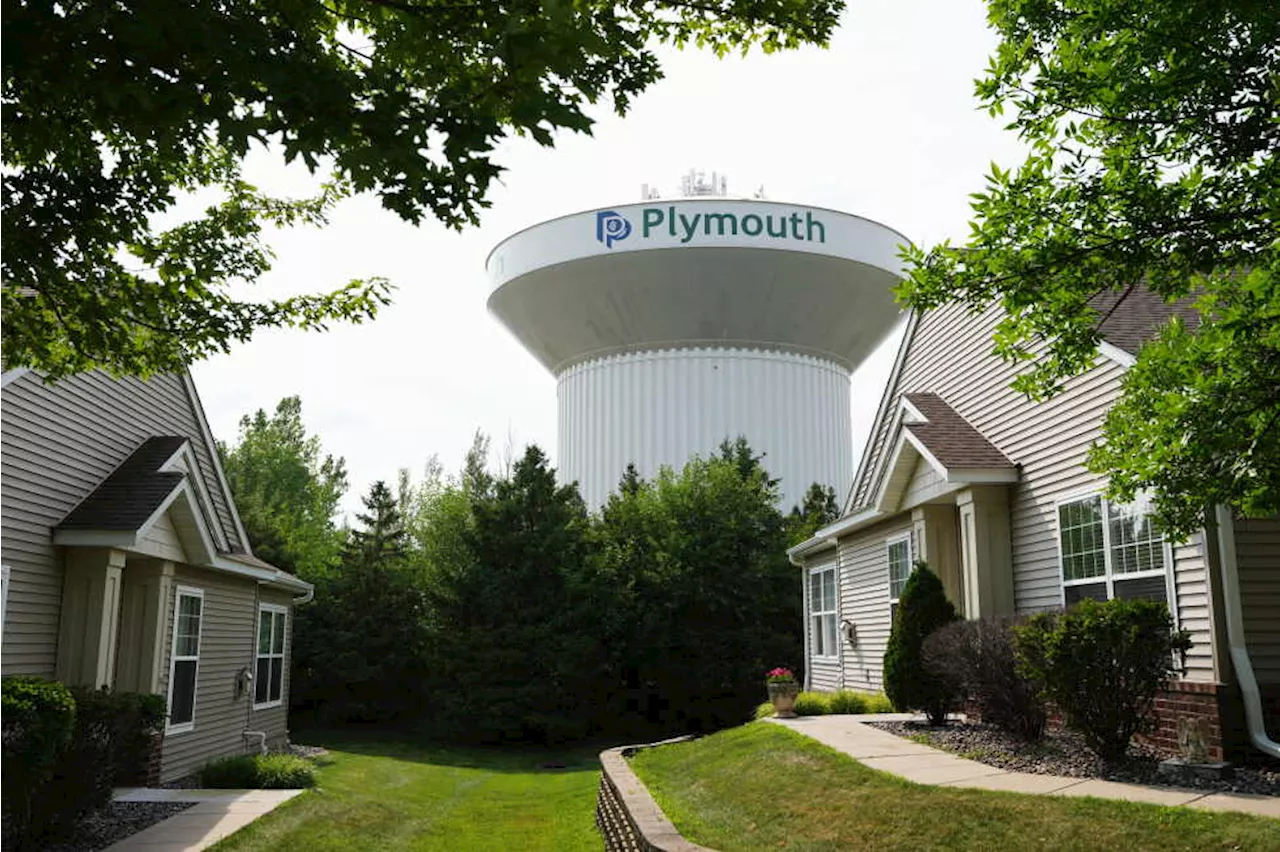
The impact was felt most acutely in the city of Plymouth and several towns along the Mississippi River, where municipal utilities reported sudden anomalies in pipeline pressure. As the report says, the resulting service outage affected a combined population of 190,000 residents, creating immediate shortages of potable water across the upper Midwest.
This event mirrors a global trend where critical infrastructure is increasingly targeted by state-sponsored or high-level criminal actors. while larger metropolitan hubs often have the resources for elite cybersecurity, the Minnesota incident highlights how smaller municipal utilities have become the "soft underbelly" of national security, where a single unpatched software flaw can jeopardize the health of nearly 200,000 people.
Governor Ann Birge’s task force and the NIST partnership
In the wake of the crisis, Governor Ann Birge has established a statewide task force to investigate the root causes of the breach and overhaul the state's cybersecurity framework. This task force will collaborate with the National Institute of Standards and Technology (NIST) and the Department of Homeland Security (DHS) to ensure Minnesota's water systems meet international resilience standards.
The state's immediate emergency directive now requires all water utilities to implement stricter access control protocols and conduct quarterly penetration tests. To ensure these measures are not merely bureaucratic, the state is integrating federal resources into a new incident response plan designed to coordinate rapid recovery efforts.
The identity of the sophisticated threat actor and the federal funding gap
Despite the scale of the attack, several critical questions remain . The source identifies the culprit only as a "sophisticated threat actor," leaving the actual identity and nationality of the attackers unknown. Furthermore, while the Minnesota Department of Health confirmed no hazardous contamination occurred, the report does not specify exactly how long the "unpatched vulnerability" had existed before it was exploited.
The incident has also highlighted a significant policy failure regarding federal support. Several lawmakers are currently arguing that state-level drinking water systems are dangerously underserved because they fall under a narrow exemption in the federal critical infrastructure framework. This exemption has historically limited the amount of federal funding available for cybersecurity upgrades in small and medium-sized utilities, leaving them to fend for themselves against global threats.
Comments 0