
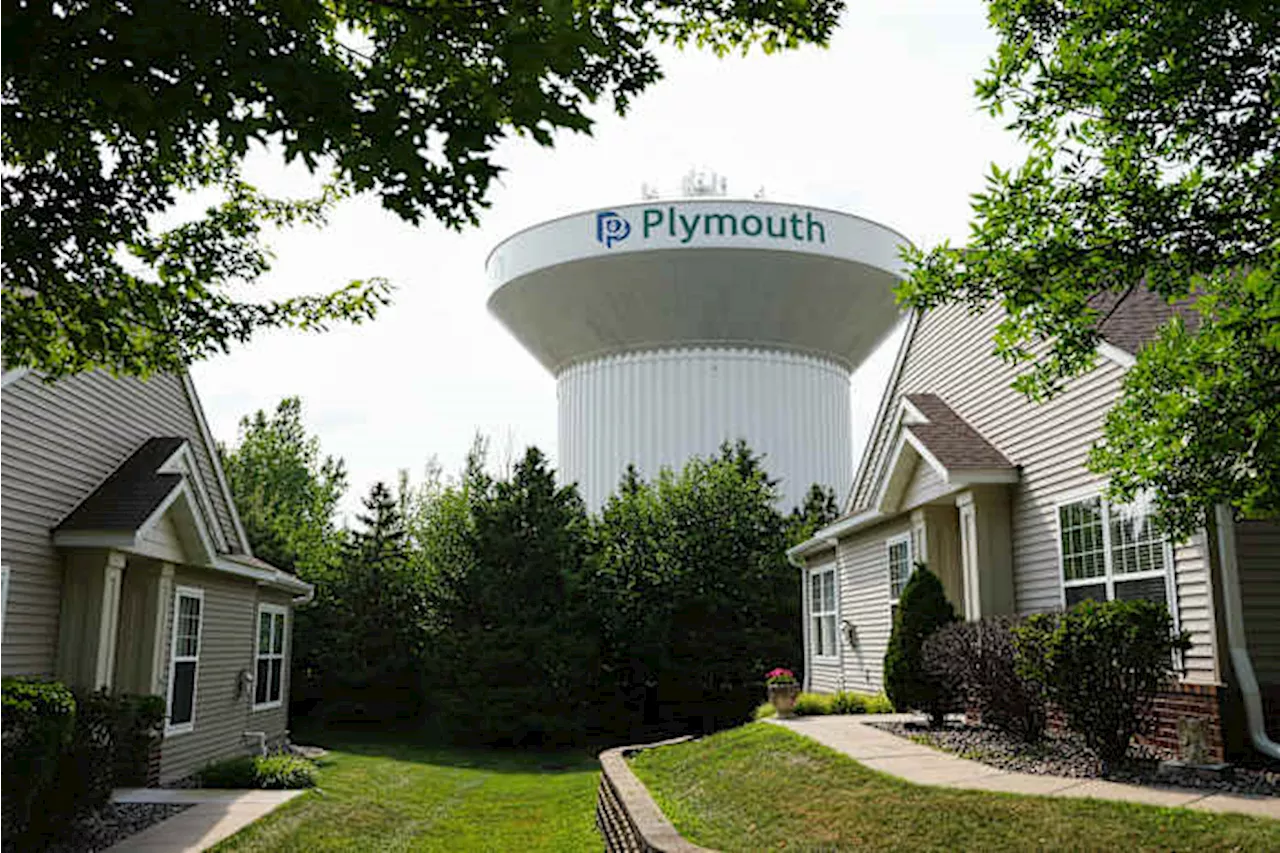
Over 30 water treatment plants across Minnesota, including the city of Plymouth, were hit by a coordinated cyberattack. State officials confirmed that while operational controls were disrupted,the drinking water remained safe for consumption.
The 30 Minnesota facilities targeted in the OT breach
The Minnesota state agency for information technology confirmed that a coordinated assault targeted the operational technology (OT) used to remotely monitor and control reservoirs, pipelines, and treatment plants. according to the report, the attackers focused on the software and communications systems, overriding or shutting down the critical operating controls that manage filtration and well pumping.
In the city of Plymouth, operators were able to prevent a total service collapse by relying on stored water in the city's water tower. This analog redundancy allowed the system to remain operational even after the strike on the digital control logic.. While the attack caused temporary outages , the report says that no affected communities experienced a total break in water delivery or any form of contamination.
How Braham's 1,700 residents were asked to conserve water
The real-world impact of the breach was felt most acutely in smaller municipalities, such as the city of Braham. With a population of approximately 1,700, Braham was forced to request that its residents conserve water for several hours while its treatment facilities were offline and under assessment.
These disruptions highlight a critical vulnerability in how municipal utilities manage their infrastructure. Because the attackers targeted the specific industrial control systems used to keep plants filtering, the only immediate solution for towns like Braham was to restrict usage until system integrity could be verified by technicians.
The FBI's warnings regarding Iranian infrastructure attacks
The FBI is currently investigating the breaches, and while the agency has not publicly named a specific suspect, its cyber division has highlighted a pattern of behavior. Intelligence suggests that Iranian actors have a documented history of targeting water and wastewater infrastructure globally, making them a primary person of interest in this coordinated event.
This incident is part of a broader, escalating trend where state-sponsored actors test the resilience of Western critical infrastructure.. By targeting the "unseen networks" of water utilities, these actors can create public panic and demonstrate the ability to disrupt basic human needs without needing to deploy physical weapons.
The funding gaps and patching failures flagged by Cynthia Kaiser
Cynthia Kaiser, a former deputy assistant director in the FBI's cyber squad and current security research executive, argues that these attacks are a symptom of systemic neglect. kaiser noted that municipal utilities are especially susceptible to such breaches due to limited funding and a lack of consistent patching capabilities for their software.
Several critical questions remain unanswered following the investigation. As the report says, investigators have not yet determined if a single group orchestrated all the incursions or if multiple actors were involved. Furthermore, it remains unclear exactly how the attackers gained initial access to the operational technology of so many disparate systems simultaneously, leaving a gap in the understanding of the state's overall cybersecurity posture.
Comments 0