
Hackers recently breached the operational technology of more than 30 water systems across Minnesota, impacting several local municipalities. While some cities have already restored their communications, the FBI is currently investigating the origin of the intrusion.
A coordinated strike on 30 Minnesota water systems
The scale of the recent cyberattack suggests a widespread attempt to compromise municipal utilities across the state. According to the report, the breach targeted the operational technology—the digital systems that manage physical processes—of over 30 different water systems in Minnesota. This type of attack is particularly sensitive because it moves the threat from simple data theft to the potential manipulation of physical infrastructure.
Minnesota IT Services has been monitoring the situation closely to determine the full extent of the damage.. As of Thursday, the agency reported that no other Minnesota communities had been forced to request changes to their drinking water usage. However, the sheer number of systems involved indicates that the attackers may have been scanning for specific vulnerabilities common to municipal water management software.
Braham's usage restrictions and Plymouth's Tuesday recovery
The impact of the breach was felt most acutely in the city of Braham, where officials had to take immediate precautionary measures. As the report notes, the city of Braham requested that its residents minimize water use while technicians worked to determine why the local water plant had gone offline. This temporary disruption highlights the immediate physical risks posed when digital controls are compromised.
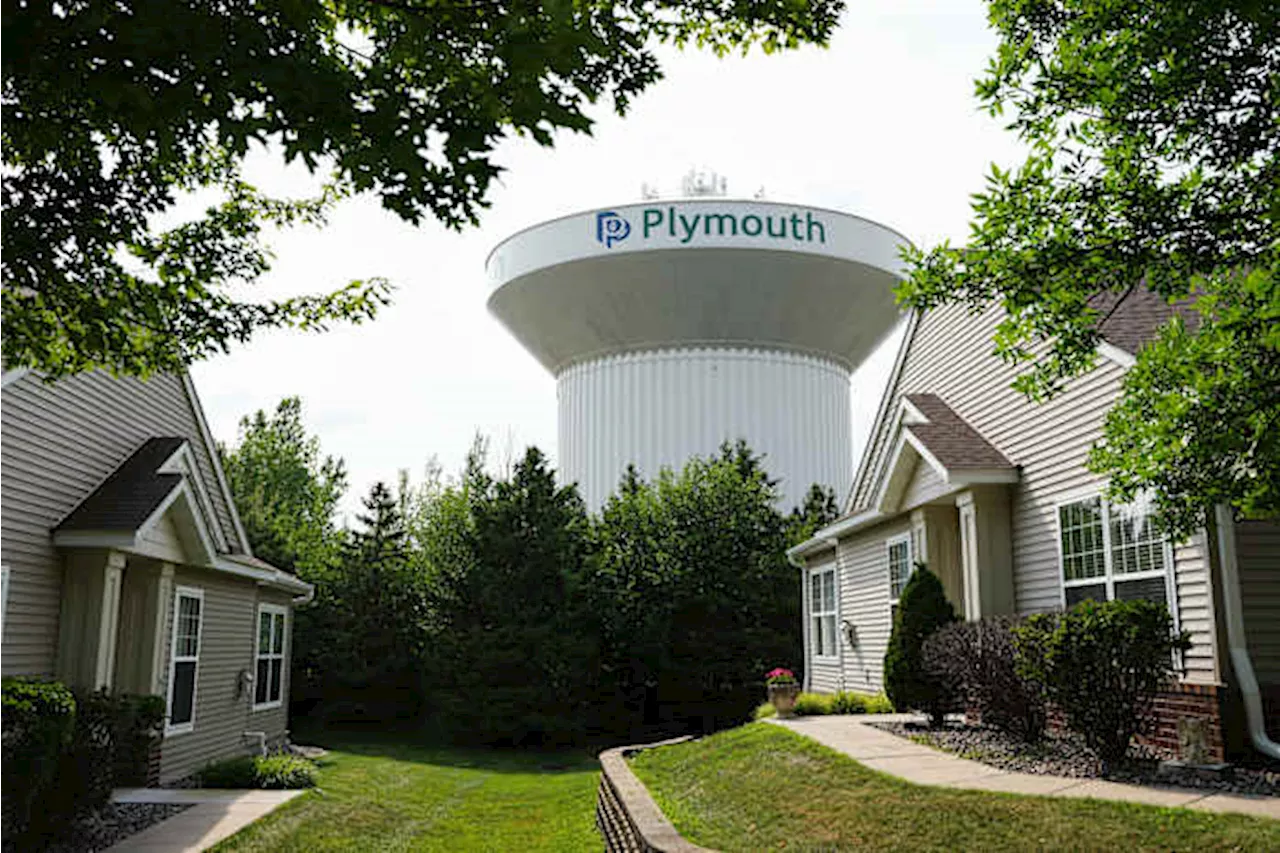
In contrast, the city of Plymouth managed to stabilize its situation relatively quickly. Officials in Plymouth confirmed that their water infrastructure communications were successfully restored by Tuesday afternoon following the initial attack. While the disruption in Plymouth was resolved within days, the incident serves as a case study for how qiuckly municipal services can be paralyzed by a targeted digital intrusion.
The FBI and CISA warnings regarding Iranian hackers
The timing of the Minnesota attacks coincides with heightened security warnings from federal intelligence agencies. Last week, the FBI and the Cybersecurity and Infrastructure Security Agency (CISA) issued an advisory warning that Iranian hackers have been actively targeting water and wastewater systems. These actors are reportedly focusing on the operational controls of critical infrastructure sectors to exert influence or cause disruption.
This broader trend of state-sponsored cyber warfare places local municipalities in the crosshairs of international geopolitical tensions. While the connection to Iran in this specific Minnesota case remains unverified,the advisory from the FBI and CISA suggests that the tactics used in Minnesota align with known patterns of behavior from foreign threat actors targeting essential services.
The FBI's investigation into an unidentified culprit
Despite the scale of the breach, the identity of the attackers remains a significant unknown. The FBI is currently leading an investigation into the incident but has not yet publicly identified a specific culprit or group responsible for the breach of the 30 water systems. This lack of immediate attribution is common in complex cyber investigations, where tracing digital footprints back to a specific actor can take weeks or even months.
One major unanswered question is whether the attackers successfully altered any chemical levels or water quality parameters, or if the braech was limited to communication and operational controls. while Minnesota IT Services has not reported any crurent needs for residents to modify their water usage, the possibility of a more deep-seated compromise of the water supply remains a primary concern for investigators and local officials alike.
Comments 0