
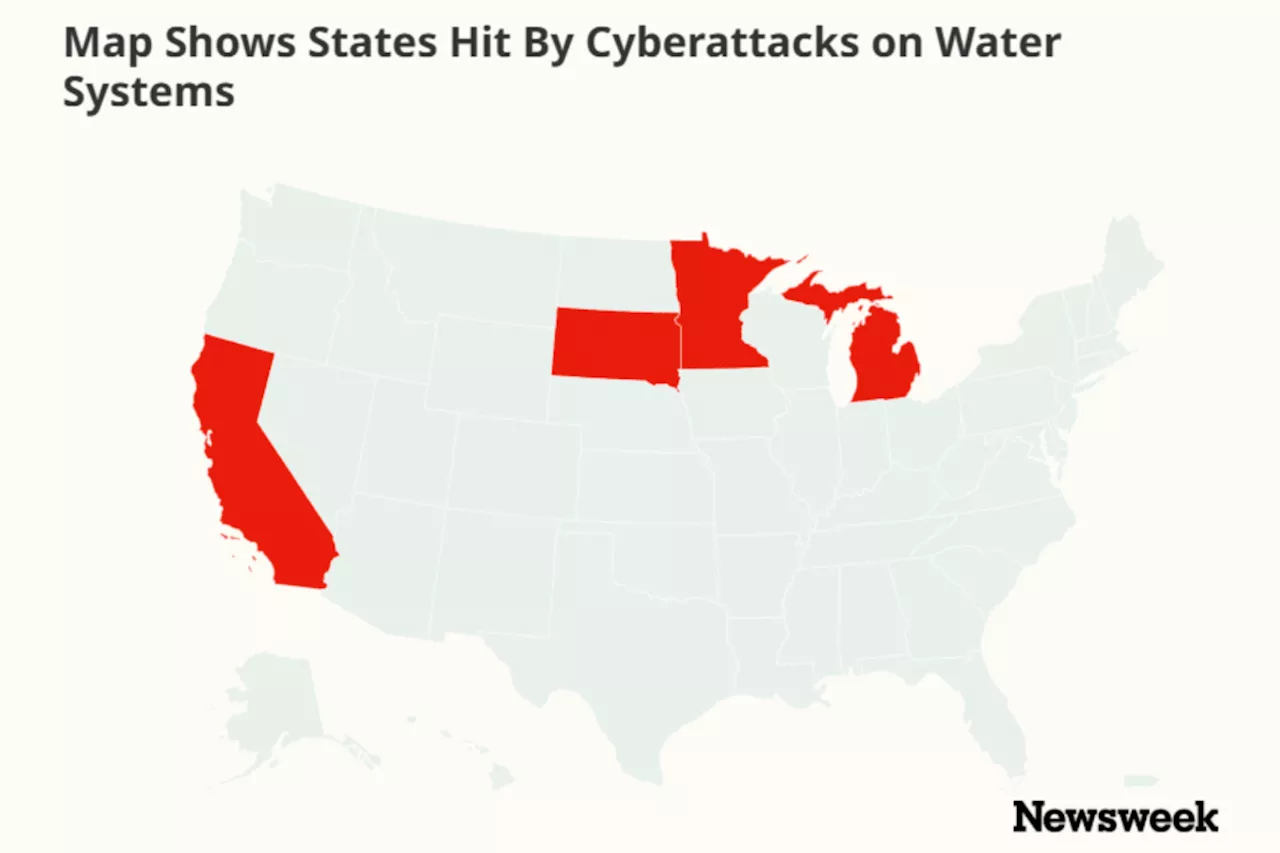
Federal agencies are investigating a wave of cyberattacks that have compromised water and wastewater systems across at least seven U.S. states. Since late July 2026, hackers have targeted critical industrial controllers, causing operational disruptions in several regions.
Minnesota's 30-system surge and the political backlash
Minnesota has emerged as a primary target in this wave of digital incursions. According to the report, state officials in Minnesota revealed that more than 30 water systems were hit by cyber intrusions, a surge that has drawn intense national scrutiny.
The scale of the Minnesota incidents has also sparked a political firestorm. President Donald Trump criticized the state's response, labeling Minnesota officials as "grossly incompetent" during the height of the security crisis. This tension underscores the high stakes involved when essential public services face digital sabotage.
Manipulated PLCs and the threat of flooding in Michigan and South Dakota
The technical nature of these attacks focuses on internet-facing Programmable Logic Controllers (PLCs), which are vital for managing industrial equipment. As the FBI reported, attackers used manipulated IP addresses and passwords to seize control of these devices, leading to risks of flooding and pressure loss.
In Michigan, the Department of Environment, Great Lakes, and Energy confirmed that cybercriminals successfully altered device settings at a wastewater facility. While the breach was contained without threatening drinking water safety, it demonstrated the vulnerability of local utilities. Similarly, in Rapid City, South Dakota, a cyberattack on a wastewater lift station required immediate intervention from law enforcement and cybersecurity experts.
Tracing the pattern back to the 2023 Aliquippa attack
Federal investigators are currently analyzing whether these recent breaches are linked to Iranian actors. The pattern of the attacks bears a striking resemblance to the November 2023 cyberattack on the Municipal Water Authority of Aliquippa in Pennsylvania, which was widely attributed to Iranian affiliates.
However, the investigation faces a significant hurdle in attribution. U.S. officials have noted that they must determine if the current attackers are truly Iranian or if another group is imitating Iranian tactics to mask their true identity. this "false flag" possibility complicates the federal response and the abiilty to hold specific nations accountable.
The mystery of the seven unnamed states
Despite the widespread nature of the crisis, several critical details remain obscured from the public. While the FBI and EPA confirmed that systems in at least seven states have been compromised since July 27, 2026, federal authorities have refrained from disclosing the full list of affected jurisdictions.
This lack of transparency leaves local providers and citizens in a state of uncertainty. It remains unknown which specific states beyond Minnesota, Michigan, South Dakota, and California are currently under threat,or whether the attackers have successfully established persistent access to other utility networks.
Comments 0