
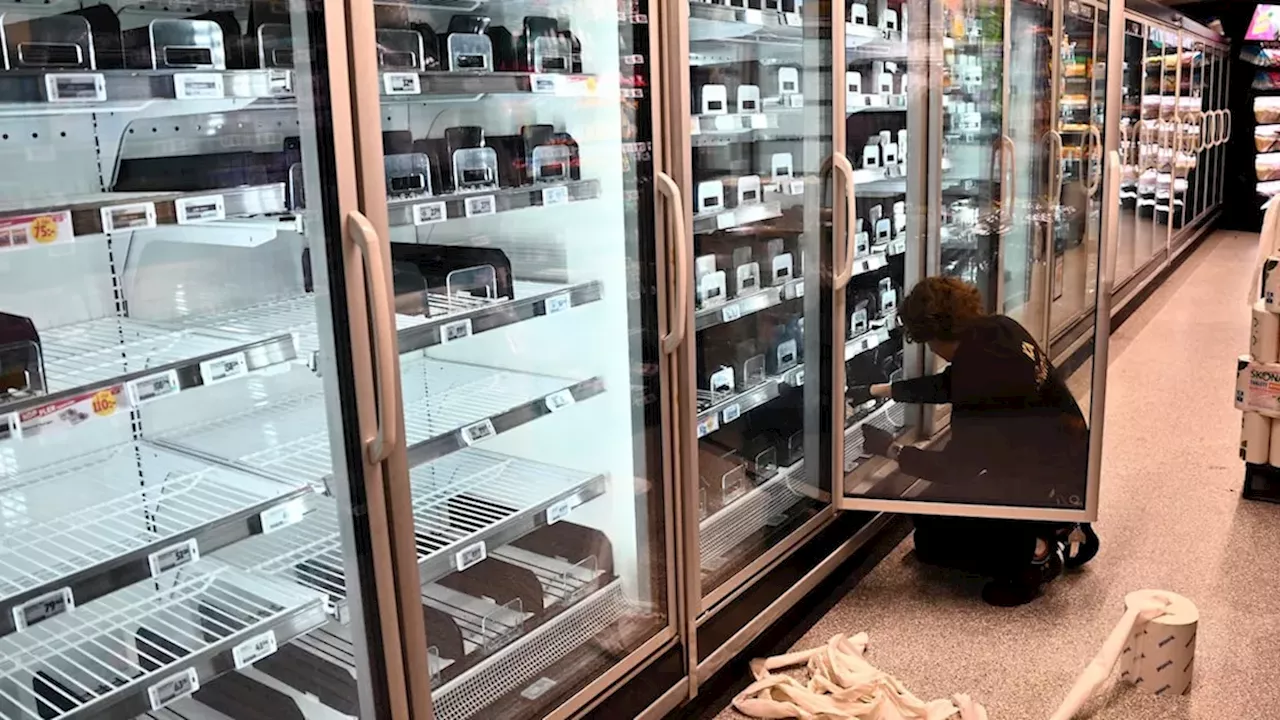
Hackers recently targeted refrigeration systems in seven European countries, including Belgium and Sweden, driving freezer temperatures as high as 50°C. These attacks caused massive food spoilage and have raised alarms regarding the cybersecurity of similar industrial equipment used in Canada.
The Danfoss vulnerability and the risk of unpatched controllers
Remote control units in large grocery stores allow maintenance firms to manage temperatures via the internet. According to the report, these units can be hijacked to fluctuate temperatures, potentially burning out equipment or spoiling food. In France, most of the hacked Danfoss controllers were older models that no longer received security updates .
This lack of patching creates a wide window for bad actors to exploit connected industrial systems. ritesh Kotak noted that any time something is connected to the internet, there is a strong possibility it could be misused by bad actors. the vulnerability in these controllers could allow hackers to manipulate everything from temperature settings to sensor data.
From grain silos to Canadian grocery aisles
Canadian infrastructure has already faced digital interference, according to reports from the Canadian Centre for Cyber Security. The agency and the RCMP have documented cases of water pressure tampering and temperature manipulation in grain-drying silos. While no Canadian grocers have reported similar spoilage, cybersecurity expert Ritesh Kotak warned that the vulnerability likely exists within Canada as well.
Metro Inc. has declined to comment on its specific cybersecurity protocols regarding these recent European incidents. Communications manager Stephane Bonk stated that the company does not publicly discuss its cybersecurity practices or controls. This silence leaves many wonedring which Canadian retailers might be utilizing the same Danfoss systems currently under threat.
Pentagon investigations and the shadow of state-sponsored sabotage
The U.S... Defense Department is currently investigating similar freezer failures at military commissaries, including an incident at Fort Huachuca in Arizona. Four officials told Reuters that the Pentagon is treating these failures as suspected hacks. These incidents mirror the European attacks, where hackers drove temperatures as high as 50°C.
Such disruptions raise fears of state-sponsored sabotage, particularly in the context of geopolitical tensions involving Russia and Ukraine. While no evidence of artificial intelligence has been found in these specific attacks, experts warn it could eventually be used to exploit unpatched systems more rapidly. The potential for ideological disruption suggests that the goal may be social instability rather than simple theft.
Who is behind the missing ransom demands?
Investigators have yet to identify a specific group claiming responsibility for the European supermarket attacks. Because no ransom demands have been made, Ritesh Kotak suggests the motive may be ideological or state-sponsored rather than purely financial. This lack of a clear financial motive distinguishes these events from typical ransomware attacks.
Several critical questions remain unanswered: which specific Canadian retailers use the vulnerable Danfoss systems, and is artificial intelligence being used to accelerate these exploits? For now, the lack of a clear perpetrator leaves the global food supply chain in a state of heightened alert, as businesses are advised to prepare for the possibility that their systems may need to go offline.
Comments 0