
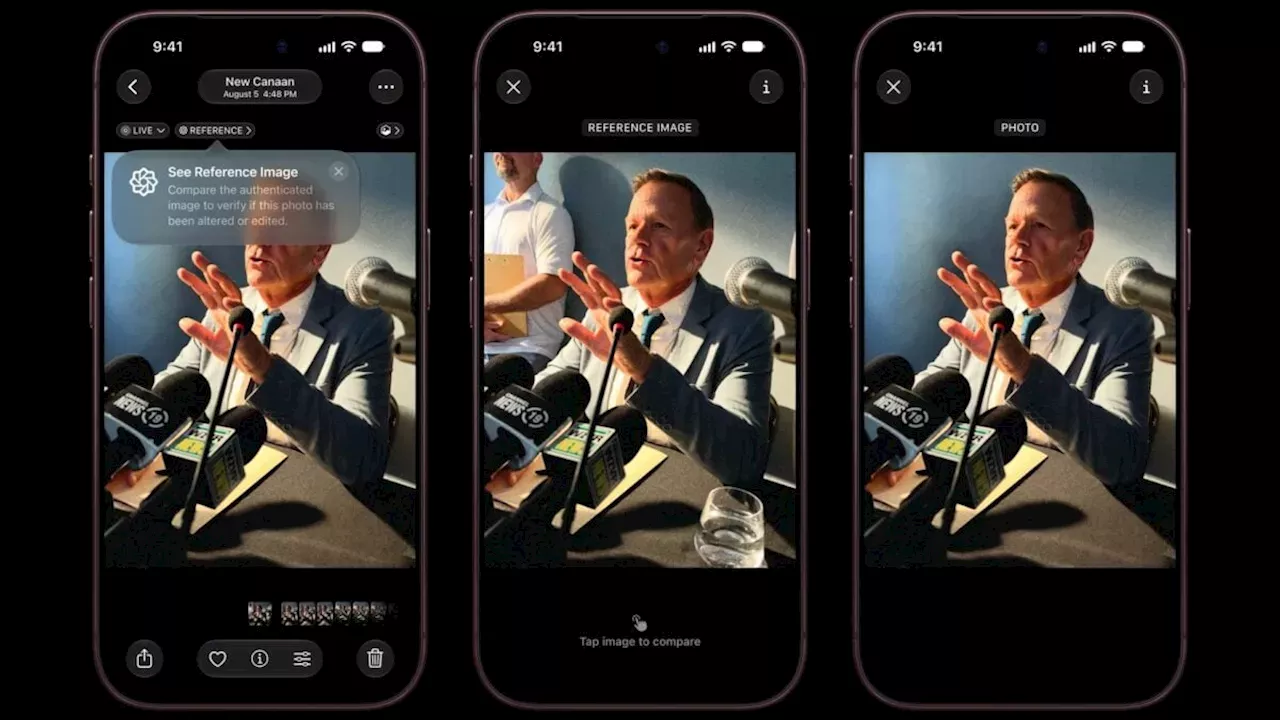
Apple has unveiled a new "Reference Image" feature for its upcoming iPhone 18 Pro series to authenticate digital photography. This technology uses a cryptographic chain to prove that images are genuine captures rather than AI-generated deepfakes.
The sensor-to-cloud chain of the iPhone 18 Pro
The authentication process for the iPhone 18 Pro begins at the manufacturing stage. according to the report, the camera sensor generates a unique cryptographic signing key the moment it first boots up. This key is then paired with a separate identity created by the device's Secure Enclave Processor.
When a user engages "Reference mode," the sensor reboots into a secure environment to sign every pixel immediately after exposure. This prevents any firmware from altering the raw data. The report notes that sensor-generated metadata, such as shutter speed and ISO, is bundled with this signed payload to ensure a complete record of the capture.
Protecting journalists and photographers from AI-generated fakes
Apple is positioning this technology as a vital tool for professionals who require visual proof of authenticity. As generative AI continues to produce convincing fake imagery, newsrooms and photographers face increasing pressure to certify their content. The "Reference Image" feature aims to provide a verifiable trail from the physical sensor to the final file .
This move reflects a broader industry-wide struggle to maintain trust in digital media. Analysts suggest that Apple's implementation could set a new standard for image provenance, potentially forcing other smartphone manufacturers to adopt similar cryptographic safeguards to remain competitive in a landscape flooded with deepfakes.
Securing the future with ML-DSA-87 and RSA-3072
To ensure the signatures remain secure against future threats, Apple is employing a sophisticated dual-layer approach.. Once the Private Cloud Compute validates the sensor and Secure Enclave identities, it processes the raw stream into a JPEG. The final signature for this file blends the traditional RSA-3072 algorithm with a post-quantum algorithm known as ML-DSA-87.
This combination is designed to protect the integrity of the image even as computing power evolves. Furthermore, Apple has included a fail-safe mechanism:if a specific sensor is ever found to be compromised, the company can revoke the signatures for images from that specific device or disable Reference mode entirely.
Uncertainties in the Private Cloud Compute verification
While the system is designed to be highly secure, several technical details remain unverified.. The report states that Apple's Private Cloud Compute validates signatures and runs a proprietary image-forensics model, yet it also claims that Apple cannot inspect the raw data directly. this raises questions about how the cloud-based forensics model can effectively confirm a "physical fingerprint" without direct access to the unencrypted pixels.
Additionally, it remains unclear how this feature will interact with third-party editing software. If a photographer uses a professional tool to adjust colors or lighting, it is unknown whether the cryptographic signature will be broken or if a new "edited" signature can be generated. Finally, the source does not specify if this verification process will be available to all users or restricted to specific professional tiers.
Comments 0