
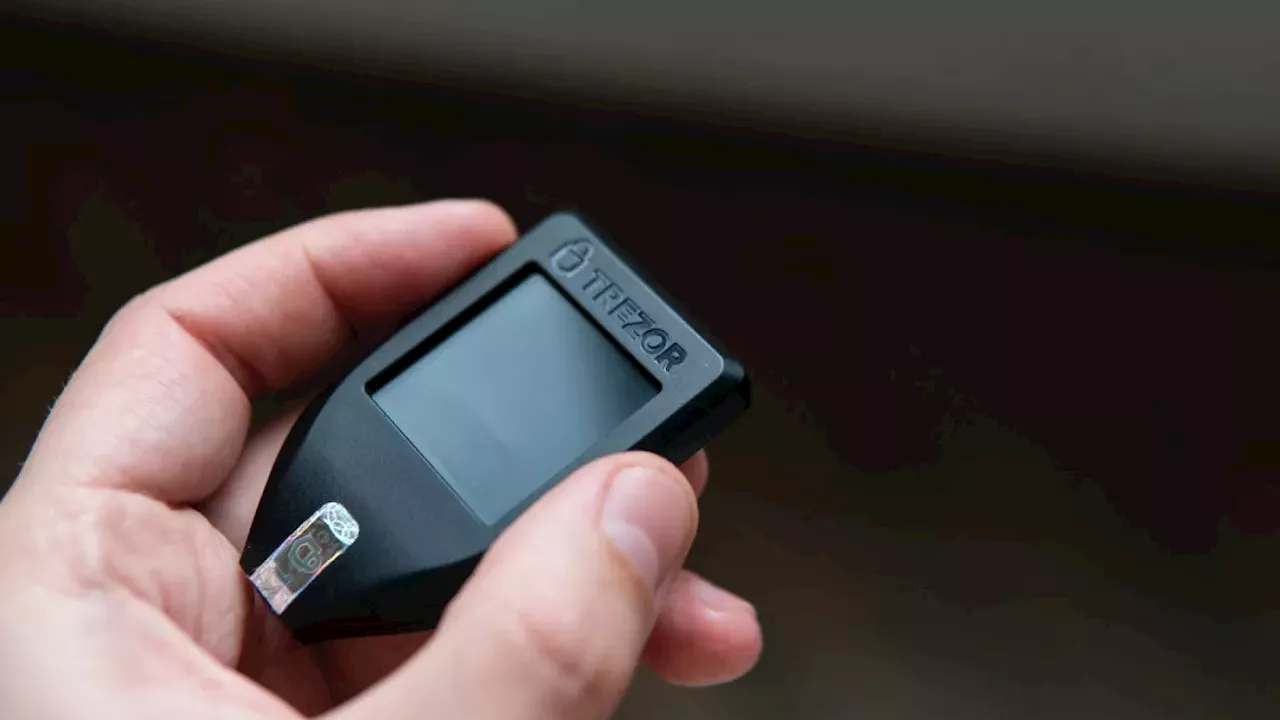
Trezor is terminating its relationships with a large number of authorized resellers by January 1, 2027, to enhance supply chain security. This strategic shift follows a massive security failure at competitor Ledger involving compromised hardware. The move aims to protect cryptocurrency users from potential device tampering before delivery.
The $90 million CryptoBilis supply-chain attack
The recent security crisis involving Ledger highlights the extreme vulnerability of hardware wallets during the distribution phase. According to the report, a Southeast Asian reseller named CryptoBilis sold Ledger devices that contained unauthorized hardware implants. These malicious components were designed to intercept the 24-word recovery phrases used by customers to initialize their wallets.
The Donjon security team at Ledger discovered that these implants could transmit stolen recovery phrases over cellular networks, bypassing traditional security layers.. While Ledger has not officially confirmed the total financial damage, on-chain sleuths estimate that the breach may have resulted in losses exceeding $90 million.
Danny Sanders and the January 1, 2027, deadline
In response to the industry instability, Trezor chief commercial officer Danny Sanders has announced a strategic pivot in how the company manages its distribution.. trezor will revoke the authorization of a significant number of its partners by January 1, 2027, as part of an effort to gain tighter control over the supply chain. This move is intended to minimize the window of opportunity for bad actors to tamper with devices before they reach the end user.
As reported, Trezor is no longer sending new inventory to the affected businesses, though these resellers are permitted to sell through their existing stock until the 2027 cutoff. Danny Sanders emphasized that this is a precautionary measure; there is currently no evidence that any Trezor hardware has been compromised in a manner similar to the Ledger incident.
The shift toward direct-to-consumer hardware security
The decision by Trezor to purge its reseller list reflects a growing trend in the cryptocurrency industry to eliminate "middleman" risks. Hardware wallets are designed to keep private keys offline, but the physical security of the device is the only line of defense before the user takes ownership. If a third-party distributor is comromised, the "cold storage" promise is broken before the device is even powered on.
This incident echoes a broader pattern of supply-chain attacks where hardware is modified at the factory or warehouse level.. By reducing reliance on authorized resellers, Trezor is effectively attempting to shorten the distance between the manufacturing plant and the customer's doorstep, reducing the number of hands that touch the device.
Which resellers face the Trezor termination notice?
Despite the scale of the announcement, several critical details remain undisclosed. The report does not specify which resellers have been flagged for termination or the total number of partners being removed from the official list. It remains unclear whether these resellers are located in specific geographic regions, such as Southeast Asia, or if the purge is a global restructuring.
Furthermore,while on-chain analysts have pointed to a $90 million loss in the Ledger-CryptoBilis case, the lack of an official confirmation from Ledger leaves a gap in the verified data. It is also unknown if Trezor plans to implmeent new verification hardware—such as tamper-evident seals or digital attestation—to replace the trust previously placed in authorized resellers.
Comments 0