
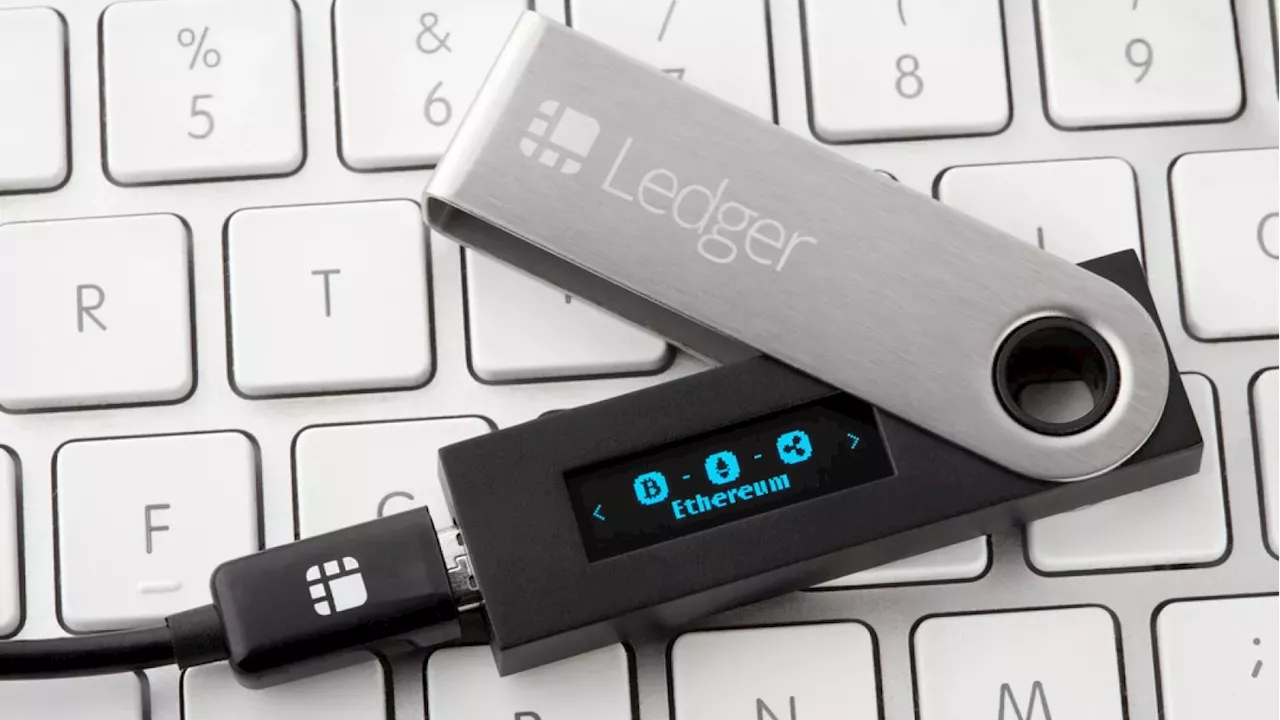
On October 9, a major cryptocurrency theft was linked to hardware devices purchased through a specific distributor. Ledger has confirmed that the compromised units originated from the Southeast Asian reseller CryptoBilis.
The CryptoBilis supply chain vulnerability
The investigation into the October 9 theft has pinpointed a specific point of failure in the hardware lifecycle. Ledger confirmed that the compromised devices were exclusively sourced from CryptoBilis, an authorized reseller operating in Southeast Asia. As a direct consequence of this breach, CryptoBilis has suspended all sales of hardware wallets. The company is currently working alongside law enforcement to investigate the theft and has reached out to the impacted customers to mitigate further damage.
This development underscores a growing reality in the digital asset space: a device's security is only as robust as the logistics chain that delivers it. Beyond its own internal fixes, Ledger has also issued a warning to other wallet providers, advising them to enhance their defenses against similar physical tampering threats.
The $86 million estimate and unverified losses
While the exact financial impact remains a subject of intense scrutiny, the scale of the incident is potentially massive. As the report notes, while Ledger has not officially confirmed a final figure , external estimates suggest that losses could exceed $86 million. This discrepancy between the unconfirmed total and the reported $86 million figure highlights the difficulty in assessing damage in decentralized environments.
For users of cold storage, these numbers represent a significant warning about the risks of "interdiction" attacks, where physical hardware is intercepted and modified before it reaches the end user. The gap between reported estimates and official company statements remains a primary concern for market stability.
A pattern of unauthorized hardware implants
This incident is not a standalone anomaly for the hardware wallet industry. ledger has previously identified instances where unauthorized hardware implants were discovered on compromised devices. this suggests a sophisticated method of tampering where attackers physically modify the circuitry to bypass security protocols. These physical attacks represent a high-level threat that bypasses traditional digital security measures entirely.
In response to these findings, Ledger has begun implementing more rigorous supply chain security measures and has updated its hardware to better resist physical tampering. This shift toward physical-layer security marks a new frontier in the ongoing arms race between hardware manufacturers and sophisticated theft syndicates.
The mystery of the undisclosed wallet count
Despite the progress in the investigation, several critical details remain hidden from the public. While Ledger has stated that the number of affected wallets is "limited," the company has refused to disclose the specific quantity of compromised users. Furthermore, it remains unclear how many other resellers might be vulnerable to similar tampering.
According to the report, the investigation also leaves open the question of whether the unauthorized implants were part of a localized issue with CryptoBilis or a broader, more systemic attack on the global distribution network. Until Ledger or law enforcement provides more granular data, the true scope of the October 9 breach remains speculative.
Comments 0